Secure Digital Examination Delivery at Scale.
Amatyas engineers computer-based testing infrastructure designed for zero-fault tolerance. Author securely, distribute globally through encrypted pipelines, and monitor candidates with advanced double-blind invigilation protocols.
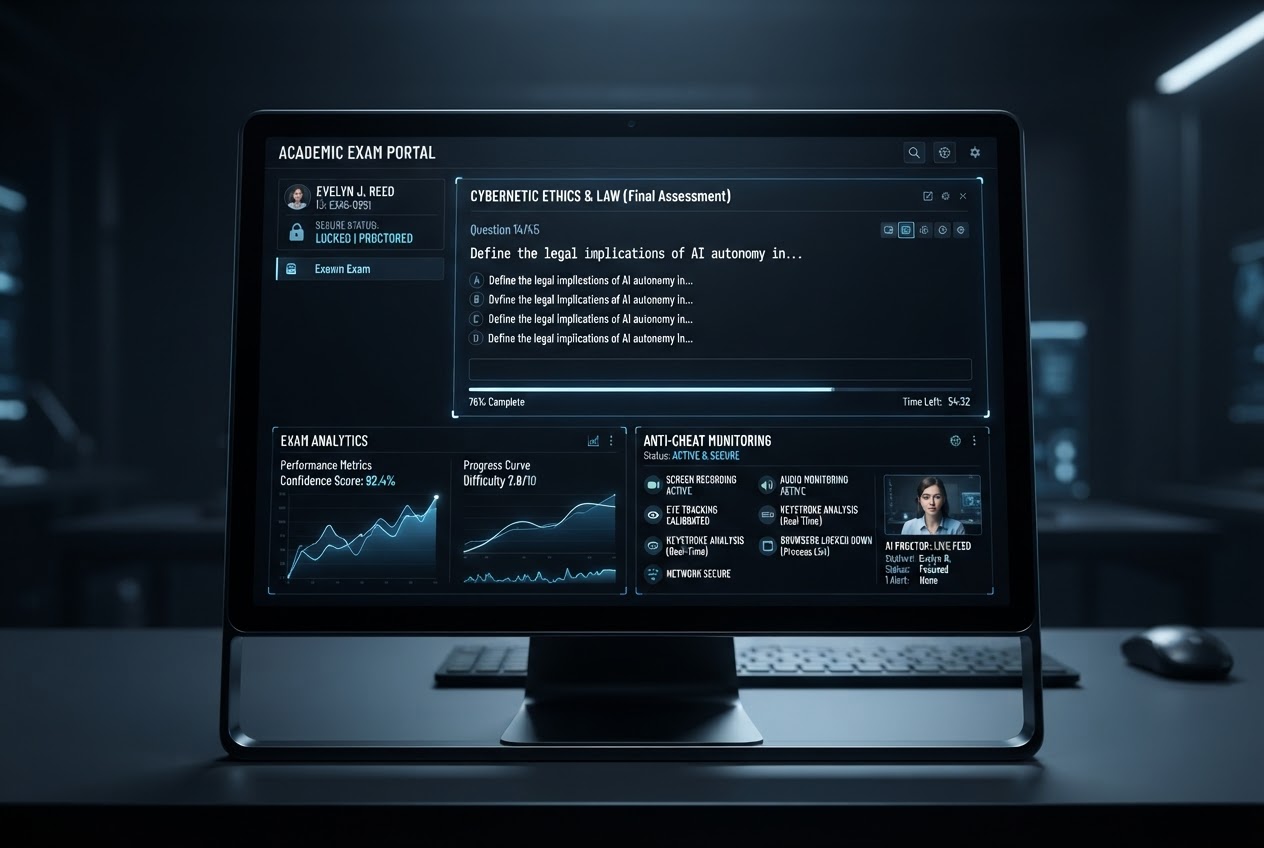
Modernizing High-Stakes Assessments
The transition from paper-and-pencil tests to computerized pipelines unlocks unprecedented structural accuracy, robust operations, and analytical oversight.
On-Demand Scheduling
Empower candidates with geographic autonomy. Provision continuous windows, flexible seat selections, and secure instantaneous slot validation.
Instant Scoring & Analysis
Eliminate weeks of manual grading latency. Run automated rubrics, psychometric calibrations, and secure parallel scoring scripts in real-time.
Adaptive Global Standards
Natively adapt cognitive difficulty levels per student response. Maximize measurement reliability with shortened, precision-mapped test lengths.
Fluid & Frictionless Candidate Journey
From registration to biometric check-in and final submission, every interface is optimized to reduce testing anxiety and maintain total operational transparency.
Seamless Registration
Candidates create profiles and schedule exams with automated reminders and clear instructions.
Biometric Check-in
Secure identity verification using facial recognition and fingerprint scanning to prevent impersonation.
Intuitive Test Interface
A clean, distraction-free environment with clear navigation and accessible tools for all candidates.
Real-time Progress
Candidates can track their time remaining and question completion status at a glance.
Transparent Results
Instant score reporting with detailed analytics and feedback to help candidates improve.
A journey designed to feel confident, not confusing
Every step is built to reduce anxiety, keep momentum high, and make the assessment feel like a clear path forward.
Unified Governance over Exam Windows
Consolidate student registration databases, eligibility matrices, center seat capacities, and individual medical accommodation rules within one enterprise cockpit.
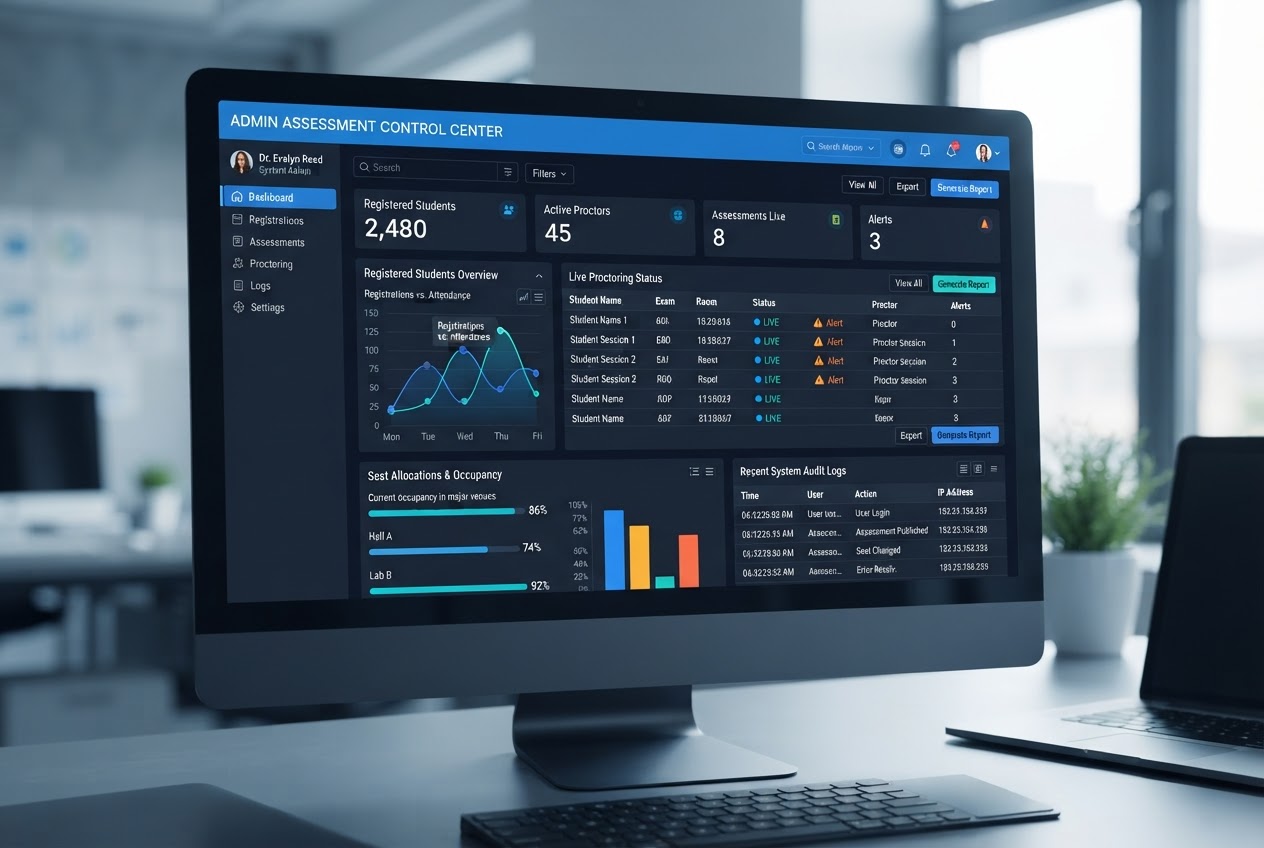
Flexible Accommodation Provisioning
Enforce accessibility options instantly. Our system supports custom time-extensions, specific high-contrast color profile toggles, compatibility with third-party screen readers, and modular administrative overrides for secure physical venues.
Accredited Physical & Virtual Venues
Secure examination centers certified through tight network constraints, audited device compliance, trained invigilator teams, and environmental parameters.
Accredited Venues
Rigorous onsite audit logs cover physical seat spaces, biometric kiosks, CCTV camera configurations, and offline recovery servers.
Secure Kiosk Provisioning
Enforce hardened hardware setups. Wipe local storage, lock BIOS configs, run sandboxed memory arrays, and block open ports before test launch.
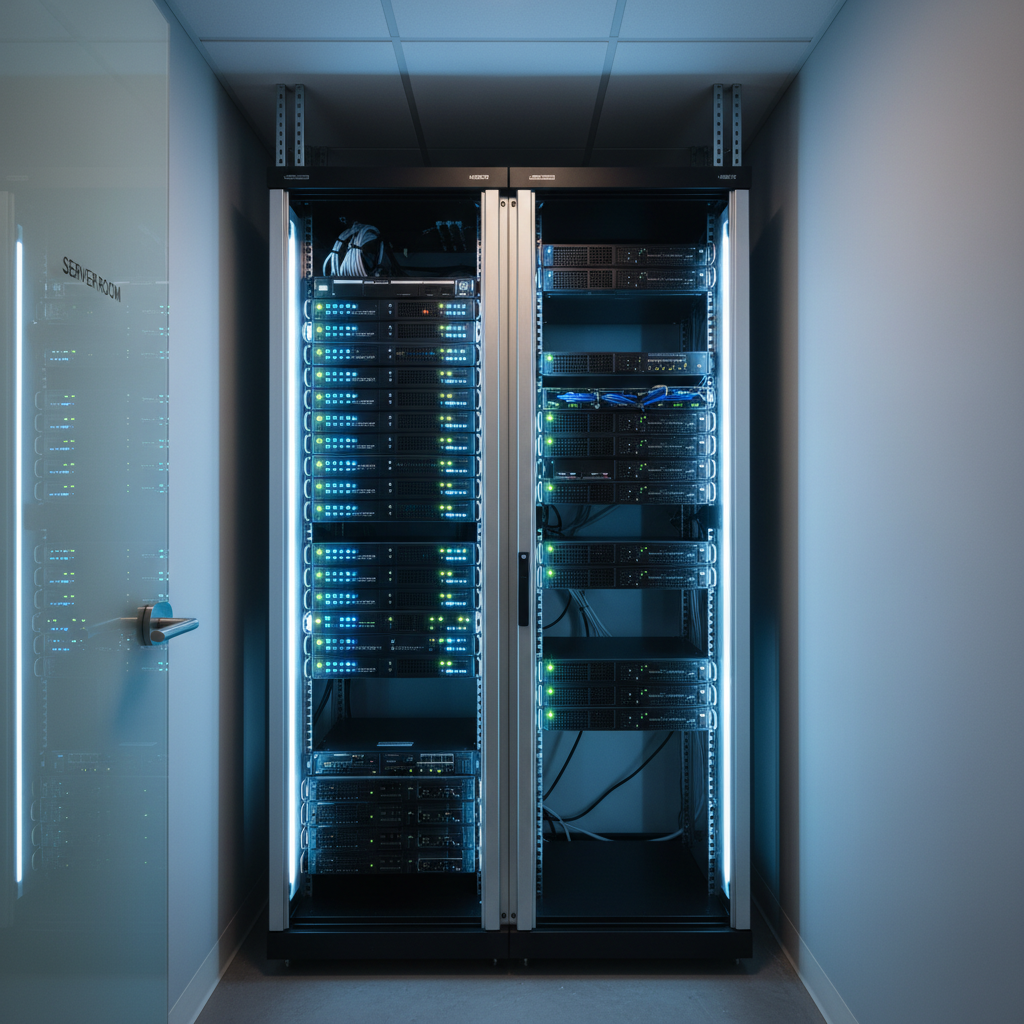
Local Offline Cache
Deliver test questions locally without internet vulnerabilities. Direct delivery caches responses on a local LAN server with continuous recovery scripts.
Examination Integrity Engineered at Every Layer.
Defense-in-depth controls protect the full assessment lifecycle — from cryptographically signed question authoring and encrypted content delivery, through biometric candidate authentication, secure browser lockdown, live behavioural monitoring, and post-exam immutable audit trail generation.
Seven Security Layers. One Unbreachable Examination.
No single control point. Security is distributed across authoring, delivery, candidate hardware, network, application, monitoring, and audit — each layer independently verified and cryptographically attested.
AUTHORING & CONTENT SECURITY
Air-gapped, role-based question authoring with multi-signature RSA-4096 custody chains. Every item is independently authored, reviewed, and approved before AES-256 encryption seals the final package.
ENCRYPTED CONTENT DELIVERY
AES-256-GCM encrypted question packages transferred over TLS-only channels. Decryption keys are time-locked — released exclusively to verified nodes within a 15-minute pre-exam window and never persisted to disk.
SECURE BROWSER & KIOSK LOCKDOWN
The exam client enforces full kiosk mode: no clipboard, no screen capture, no external drivers, no unauthorised network routes. Process injection attempts trigger immediate session termination and admin alerts.
LIVE MONITORING & INCIDENT RESPONSE
AI-assisted behavioural analytics flag gaze deviation, audio anomalies, and process violations in real time. Proctors receive prioritised incident queues with one-click escalation paths and evidence capture for post-exam review panels.
AUDIT TRAILS & POST-EXAM INTEGRITY
Every administrative action, candidate event, and system state change is written to an append-only, cryptographically chained audit log. Post-exam integrity checks validate response data against server-side hashes before any scoring pipeline begins.
Multi-Signature Custody Chain — Author to Encrypted Package.
No question paper exits the authoring environment without independent RSA-4096 signatures from Author, Reviewer, Approver, and Package Creator. Only when all four signatures are verified does the AES-256 encryption envelope seal the final package for distribution.
Ciphertext and Key — Always Separated, Always Controlled.
Question packages travel as ciphertext. Decryption keys travel on an entirely separate, time-gated asymmetric channel. The two streams converge only inside the candidate's verified RAM enclave — never on disk, never in transit together.
Encrypted Content Pre-Staging
AES-256-GCM encrypted question packages are pre-staged to exam centre local servers 24 hours before the window opens. Without the corresponding time-locked decryption key, the payload is cryptographically inert — zero examination data is exposed during staging.
Time-Locked Key Release
RSA-4096 decryption keys are generated on air-gapped administrative nodes and held in offline escrow until T-15 minutes. Release is triggered automatically by the exam clock — dispatched over certificate-pinned TLS exclusively to attested candidate nodes. Any clock manipulation invalidates the release.
Volatile RAM Execution & Secure Wipe
Question payloads are decrypted exclusively into a locked RAM enclave — no disk write is permitted. On final submission, the enclave is cryptographically wiped. No examination content survives the session on the candidate workstation under any failure condition.
Zero-Trust Exam Server Infrastructure.
Exam servers operate inside a zero-trust network perimeter. No human login access is permitted during active windows — all administrative actions require decentralised multi-signature authorisation. Full-disk encryption, automated build verification, and live telemetry pipelines to the Command Centre ensure continuous integrity.
Air-Gapped, Human-Free Administration
Ground personnel hold zero infrastructure permissions during live exam windows — eliminating insider threat vectors entirely. Server parameters are loaded via decentralised multi-signature keys. Any unauthorised access attempt triggers an automatic shutdown and generates a signed incident report for forensic review.
Live telemetry and anomaly signals are tunnelled back to the central Command Centre via encrypted APIs. Interventions require triple-entity physical keys.
Hardened Candidate Node — Trusted Boot to Session End.
Every candidate workstation boots from a cryptographically signed, diskless OS image loaded directly into volatile RAM. The exam application runs inside an isolated memory enclave with all external ports locked, all background processes killed, and continuous intrusion detection active throughout the session.
Verified Boot — Only Attested Hardware Enters the Exam.
Our custom PXE network boot environment performs UEFI Secure Boot verification and CPU hardware attestation before releasing any exam OS. Workstations with unrecognised hardware signatures, modified firmware, or invalid device IDs are refused immediately — the refusal event is logged to the audit chain and the proctor is alerted in real time.
Trusted Boot Handshake
Node parameters match local registrations exactly. PXE payload decryption triggers locally in volatile sandbox registers.
Access Denied & Logged
Foreign kernel parameters or invalid device ID detected. Connection closed instantly at hardware network interfaces.
Custom PXE Network Boot
No local media storage required. The operating system image is dispatched dynamically to volatile RAM pools via hardened local servers.
HTTPS Encrypted Delivery
OS images are enveloped in TLS tunnels with certificate pinnings to avoid packet manipulation or network sniffing.
Hardware-Signature Check
Each device's CPU signature and UEFI variables are verified against administrative registries before any bootstrap release.
Every Candidate. Every Seat. Every Action — Audited.
Double-blind biometric matching, algorithmic seat randomisation, and cryptographic node binding are all captured as immutable audit events. No seat can be pre-assigned, overridden, or swapped without a multi-authority authorisation trail that regulatory bodies can independently inspect.
Manual override of randomised seat placement is strictly locked. Any workstation modification logs an audit event directly to regional controller networks.
Live Monitoring, Incident Response & Audit — Throughout Every Session.
AI-assisted proctoring continuously analyses video feeds, audio levels, gaze patterns, and system events across all active nodes simultaneously. Prioritised incident queues give proctors immediate context — flagged events are timestamped, evidence-captured, and appended to the post-exam audit package without interrupting the candidate.
Ten Verified Controls. Zero Single Points of Failure.
Amatyas secures every node in the assessment lifecycle independently — each stage cryptographically attested, each control auditable. Compromise of any single layer cannot expose the full examination chain.
Ready to Audit Our Security Architecture?
Engage our security team for a full technical briefing — covering cryptographic protocols, candidate authentication flows, live monitoring controls, incident response playbooks, and post-exam audit trail structure. We welcome scrutiny from boards, regulators, and independent assessors.
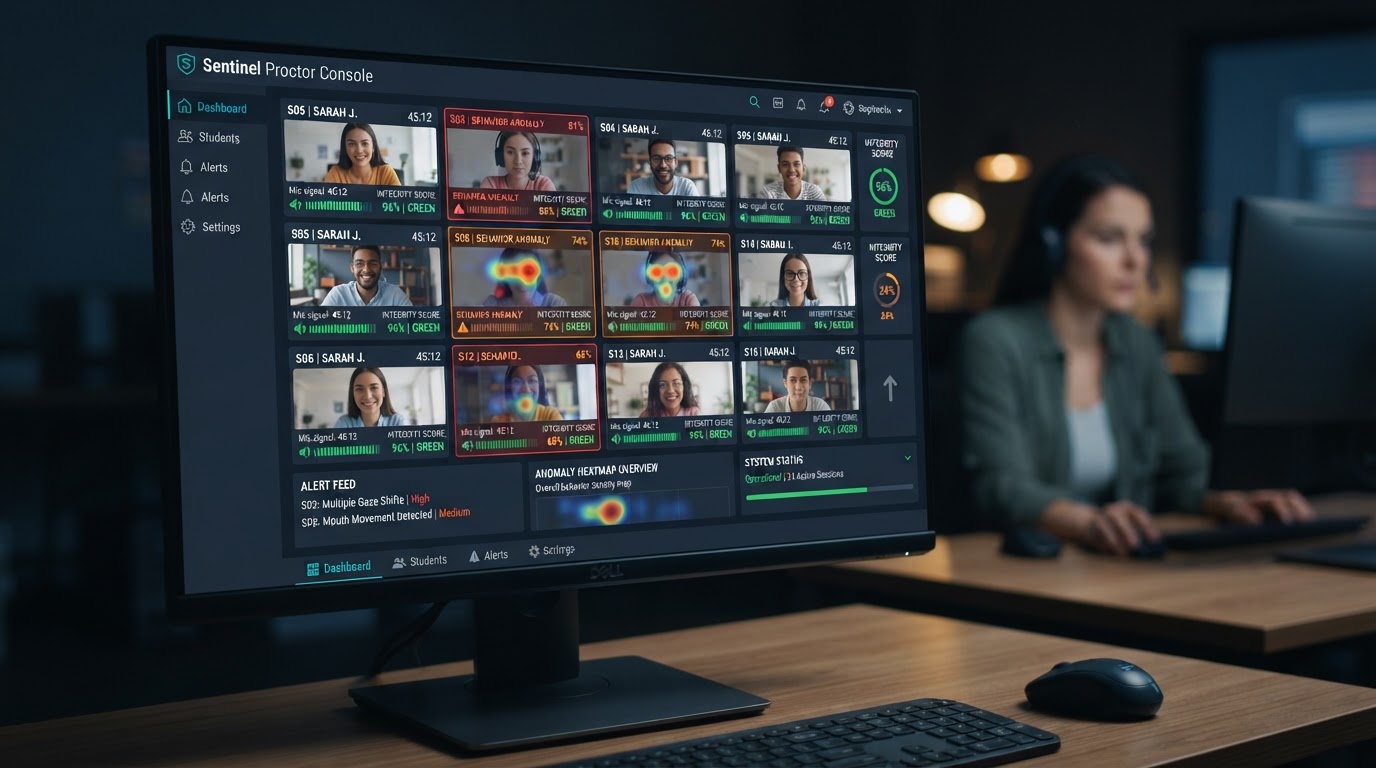
AI-Assisted Live Monitoring & Incident Response
Continuous behavioural analytics surface gaze deviation, audio anomalies, and secure browser violations to proctors in real time. Prioritised incident queues with one-click evidence capture ensure every flagged event is documented, escalated, and preserved for post-exam adjudication.
Continuous Behavioural & System Monitoring
AI proctoring analyses video feeds, microphone levels, gaze vectors, and OS process events simultaneously across all active candidate nodes. Anomaly signals are scored, ranked by severity, and surfaced to proctor dashboards without interrupting the candidate session. All flagged events — with timestamped evidence snapshots — are appended to the tamper-proof post-exam audit package.
- AI Behavioural Anomaly Detection
- Secure browser & process violation alerts
Granular Testing Rules & Configs
Tailor the testing application precisely to the structure of your boards, technical certifications, or language requirements.
Modular Time Limits
Configure overall exam duration, fixed-duration sections, or adaptive timing variables at the individual question level.
Linear / Free Navigation
Define whether candidates can freely cycle between sections, flag items for review, or are forced along a strict one-way answer path.
Embedded Reference Tools
Integrate native scientific calculators, digital scrappads, and standard reference formula PDFs safely within the secure sandbox.
Resilient Final Submission Pipelines
Ensure zero packet loss during final answer packet transmissions. Protect results against structural crashes, browser exits, or unstable WAN links.
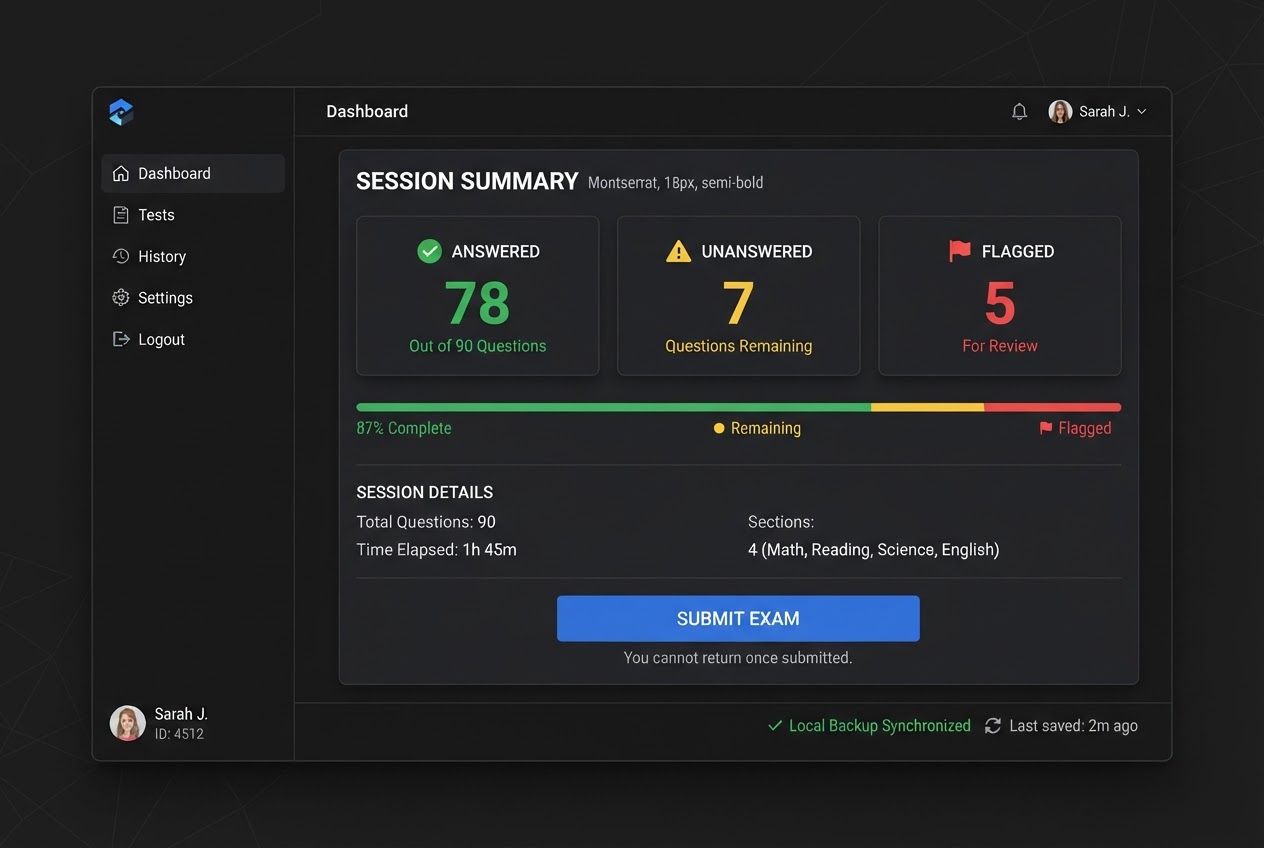
Continuous local caching failsafes
Every answer choice selected is instantly saved to three physical locations: local client RAM sandbox, encrypted client disk cache, and the test center's local local-network backup server. If a workstation goes dark, the session resumes instantly on another terminal with zero progress lost.
Automated Score Delivery & Analytics
Integrate result streams directly with corporate registries, university portals, psychometric calibration suites, and HR database pipelines.
Psychometric Calibration
Determine standard difficulty indices, item discrimination factors, and point-biserial statistics automatically across testing cohorts.
Restricted API Hubs
Deliver secure XML transcripts and raw response records directly to institutional HR, student CRM databases, or global registries.
Managed Score Release
Secure embargo configurations protect final transcript arrays until structural normalization runs have cleared administrative approval.
Empirical Success Stories
Review how national boards, premiere associations, and high-throughput universities engineered reliability into their testing systems.
National Licensing Board — 1.2M+ Candidates
A national professional licensing board migrated their full paper-based examination inventory to Amatyas' CBT platform. Cryptographic audit trails satisfied the regulator's independent security review. Score release latency dropped from 6 weeks to 48 hours, with zero data integrity incidents across three consecutive examination cycles.
Medical Council — High-Stakes Clinical Assessment
A national medical council deployed Amatyas across 47 accredited regional centres. Double-blind biometric check-in, randomised question compilation, live AI proctoring, and post-exam cryptographic response validation together satisfied the council's ISO 27001 audit requirements. Zero security breaches recorded across all sessions.
Discuss Your High-Stakes Examination Security
Whether you are transitioning a national examination board, deploying secure professional licensing assessments, or seeking an independently auditable CBT partner — our security engineers will map a cryptographically sound solution to your specific regulatory and operational requirements.